FCA finalises cryptoasset perimeter guidance ahead of authorisation gateway
The FCA’s final perimeter guidance makes UK crypto authorisation an activity-level question before applications open on 30 September.

What happened
On 16 September, the Financial Conduct Authority published PS26/18, its final guidance on when activities under the UK’s future cryptoasset regime require FCA authorisation. The guidance is incorporated into the FCA’s Perimeter Guidance Manual as PERG 18 and follows 78 responses to the earlier consultation.
The perimeter assessment covers whether an activity is carried on by way of business in the United Kingdom and which permission may be required. The regulated activities include issuing qualifying stablecoins in the UK; safeguarding or arranging the safeguarding of qualifying cryptoassets; operating a qualifying cryptoasset trading platform; dealing as principal or agent; arranging deals; and arranging qualifying cryptoasset staking. Cryptoasset lending and borrowing may also fall within the dealing or arranging activities, depending on how the service operates.
This is distinct from the policy package published in June. Those statements set out the rules firms must follow once they are within the regime. PS26/18 addresses the prior question: whether the substance of a firm’s activities places it inside the perimeter and, if so, which permissions it needs.
The regime is due to take effect on 25 October 2027. The application window opens on 30 September 2026 and closes on 28 February 2027 for firms that want to use the relevant savings provisions. Existing registrations and permissions will not convert automatically. Firms registered under the Money Laundering Regulations, firms already authorised under FSMA, and payment or electronic-money institutions may still need new authorisation or a variation of permission for the cryptoasset activities they perform.
The guidance is also relevant to overseas firms providing cryptoasset services to UK consumers, as well as traditional financial firms entering crypto markets. The legal entity’s location therefore cannot be assessed without considering what it does, for whom and where the activity is treated as taking place.
The FCA expects to consult on targeted amendments to the guidance later in 2026 following changes to the underlying legislation, with final amended guidance expected in early 2027. The current guidance can be used for most authorisation preparations, but firms affected by areas such as stablecoins, proprietary trading, technical services, decentralised arrangements and safeguarding will need to follow those updates.
Why it matters for KYB teams
PS26/18 makes clear why “FCA regulated” cannot be treated as a single company-level attribute. One legal entity may operate a trading platform, safeguard customer assets and arrange staking, while holding—or applying for—permission for only some of those activities.
The perimeter analysis also depends on substance rather than marketing terminology. Descriptions such as “wallet,” “platform,” “exchange” or “technology provider” do not by themselves establish the regulatory outcome. KYB teams need enough evidence about how the service actually works, which entity performs each role, whether UK consumers are served and where control over the activity sits.
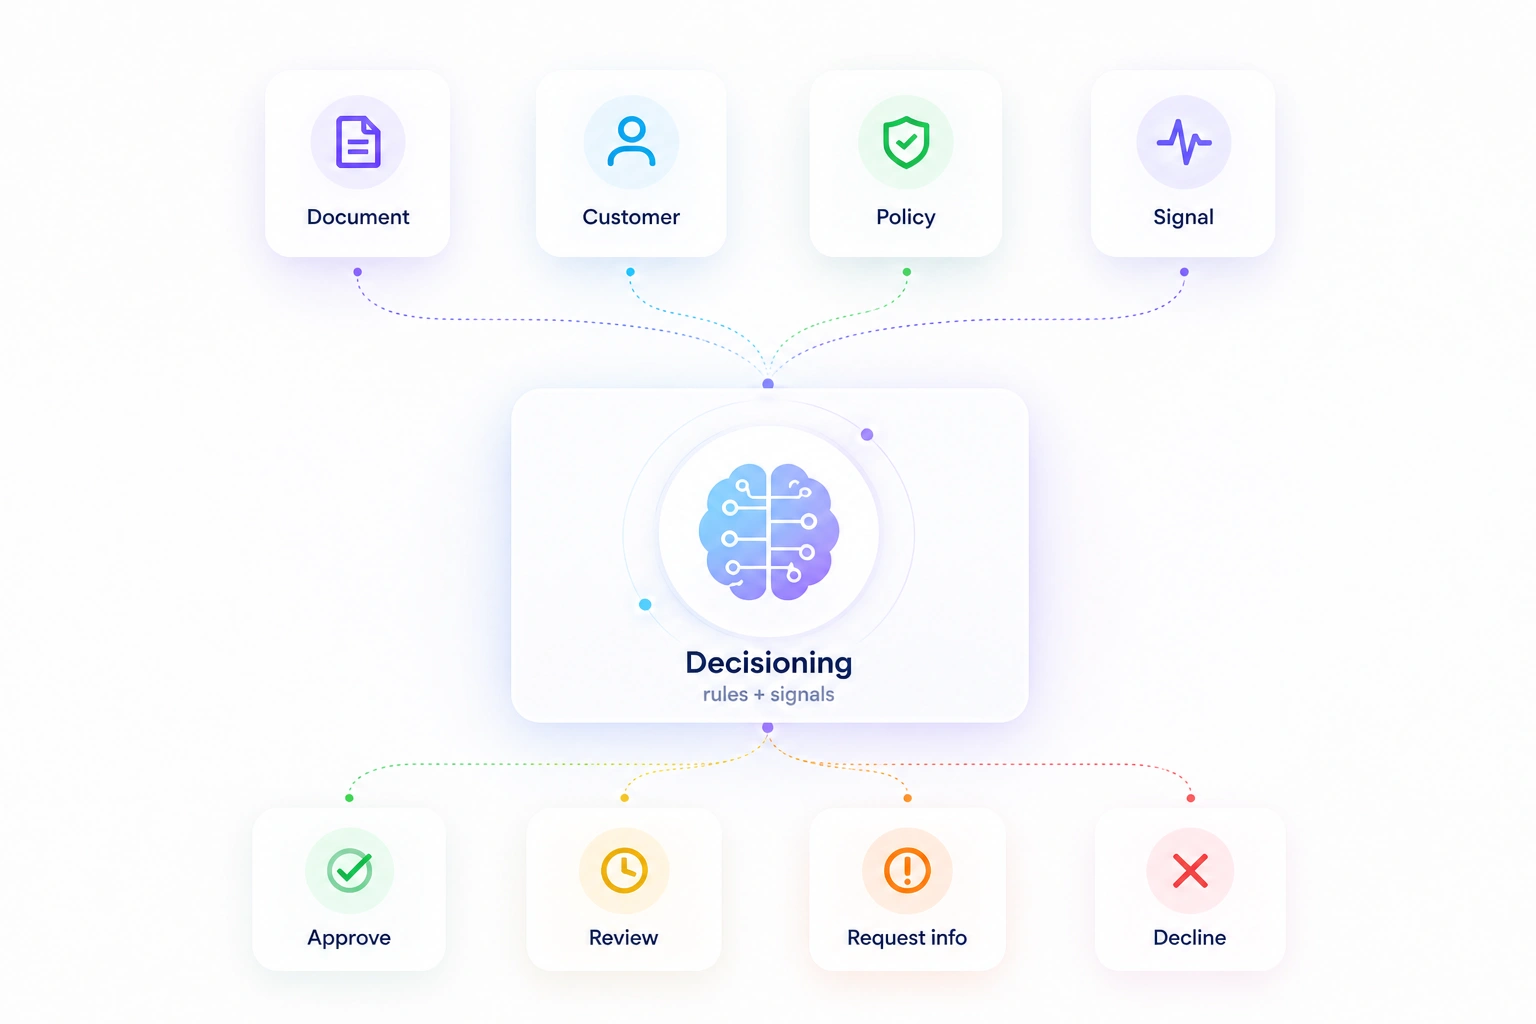
For firms onboarding VASPs or other crypto counterparties, the practical task is to connect the business model to the precise regulatory evidence. A robust crypto KYB workflow should distinguish MLR registration, existing FSMA authorisation, a new permission, a pending application and reliance on a transitional provision. None should silently substitute for another.
This is not only an onboarding question. A counterparty may add custody, staking or stablecoin services, begin serving UK customers, move an activity to another group entity or receive a different authorisation outcome. Those changes can alter the perimeter assessment even when the company name and registration number remain unchanged. Ongoing monitoring therefore needs to cover changes in services, operating footprint, responsible entity and permission status—not only sanctions or corporate-registry events.
The defensible KYB conclusion is consequently activity-specific and time-stamped: this legal entity was assessed for these services, in this market, against this evidence and permission status on this date. Where the position remains uncertain or further guidance is pending, that limitation should remain visible in the decision record.
What teams should review
- Are all UK-facing crypto services mapped to the specific legal entity that performs each activity?
- Does the review assess what the business does in practice rather than relying on labels such as “exchange,” “wallet” or “technology provider”?
- Can the workflow distinguish MLR registration, existing FSMA authorisation, additional permissions, a pending application and transitional status?
- Are trading-platform, safeguarding, stablecoin, dealing, arranging and staking activities checked against the precise permission scope?
- Do overseas counterparties receive a documented UK territorial assessment when they provide services to UK consumers?
- Can new products, changes in customer geography, transfers between group entities or permission-status changes trigger reassessment?
- Are the source, date, rationale and unresolved limitations behind the perimeter conclusion preserved in the audit trail?
- Is there an owner for reviewing the FCA’s next targeted perimeter-guidance consultation and updating affected cases?